Learn what social engineering is, how cybercriminals manipulate people, common attack methods, and simple ways to protect yourself online.
When we hear about cyber attacks, we often picture hackers breaking into computers, exploiting software bugs, or spreading malware. But sometimes, attackers don’t need to break through a technical security system at all. They simply convince someone to open the door for them.
That’s the idea behind social engineering.
Social engineering is a cybersecurity technique that relies on manipulating people into revealing information, giving access, sending money, or taking an action that benefits an attacker. Instead of attacking technology directly, the attacker targets human behavior.
What Is Social Engineering?
In simple terms, social engineering is the use of deception and manipulation to trick people.
An attacker might pretend to be a bank employee, IT support worker, delivery company, colleague, or even a friend. They may then ask for a password, verification code, payment, or access to an account.
For example, imagine getting a call from someone claiming to work for your company’s IT department. They tell you there’s an urgent problem with your account and ask for the verification code sent to your phone.
The story may sound believable, especially if the caller knows a few details about you or your workplace. But handing over that code could give the attacker access to your account.
Social engineering can happen through email, text messages, phone calls, social media, websites, or face-to-face interactions.
How Do Social Engineering Attacks Work?
Although the methods vary, many attacks follow the same basic pattern.
1. The attacker builds trust
They may impersonate someone you recognize or someone who appears to have authority.
2. They create pressure
The attacker might claim there’s an emergency or give you a very short deadline. The goal is to make you react instead of stopping to investigate.
3. They ask you to do something
You might be asked to click a link, open an attachment, share a password, provide a verification code, transfer money, or approve an account request.
4. They use the information or access
Once you take the requested action, the attacker may use what you’ve provided to steal an account, money, personal information, or access to a larger system.
Attackers may also research their targets beforehand. Information shared publicly on social media or company websites can sometimes help them create more convincing stories.
Common Types of Social Engineering
Social engineering isn’t limited to one particular type of scam.
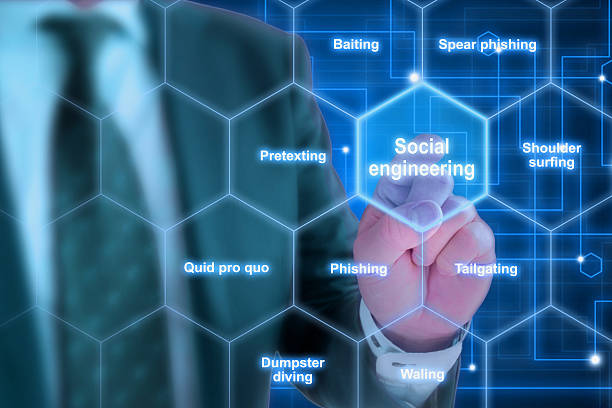
Phishing
Phishing uses fake emails, websites, messages, or other communications to trick people into revealing information or taking an unsafe action. It’s one of the most common forms of social engineering.
Pretexting
With pretexting, the attacker creates a believable story to justify their request. They might pretend to be a customer, employee, bank representative, or technical support agent.
Baiting
Baiting uses something tempting to encourage a person to take an action. That could be a fake download, an attractive offer, or even a physical device such as a USB drive.
Quid Pro Quo
Here, the attacker offers something in return for information or access. For example, someone might pretend to provide technical support in exchange for login details.
Why Does Social Engineering Matter?
Technology can protect your accounts and devices, but it can’t always stop you from voluntarily giving information to the wrong person.
That’s why social engineering remains an important cyber security concern. An attacker doesn’t necessarily need to exploit a complicated software vulnerability if they can convince someone to bypass a normal security procedure.
The consequences can include stolen accounts, financial fraud, data theft, malware infections, and unauthorized access to business systems.
How Can You Protect Yourself?
You don’t need to be a cybersecurity expert to make social engineering attacks harder to succeed.
A few simple habits can go a long way:
-
Slow down when something feels urgent. Pressure is often part of the trick.
-
Verify unexpected requests. Contact the person or organization using a trusted phone number, app, or website.
-
Never share passwords or verification codes.
-
Think before clicking links or opening attachments.
-
Be careful about what personal information you share publicly.
-
Use multi-factor authentication on important accounts.
-
Report suspicious messages or calls when appropriate.
The most important habit is to question unexpected requests, particularly when someone asks you to bypass a normal security process.
Conclusion
Social engineering is a cyber security threat that targets people rather than just computers. Attackers use trust, urgency, fear, curiosity, or helpfulness to persuade people to do something that puts their information or accounts at risk.
The good news is that one of the simplest defenses is also one of the most useful: pause and verify.
If an unexpected email, text, phone call, or online message asks you to share sensitive information or act immediately, take a moment to check who is really behind it. A few extra seconds can prevent a much bigger problem.
External Sources/Links
FAQs
Is social engineering a cyber attack?
Yes. Social engineering is used in cybersecurity attacks to manipulate people into revealing information, granting access, transferring money, or taking other actions that benefit an attacker.
Is phishing a form of social engineering?
Yes. Phishing is a common form of social engineering that uses deceptive communications to trick people into revealing information or interacting with malicious or fraudulent content.